← All work
Basmah ISMS
A multi-client workspace where a consulting firm runs ISO 27001:2022 certification projects end to end: context and scope, gap assessment, Statement of Applicability, controls and evidence, risk register, audits, and documents, in Arabic and English.
- Designed and built the platform
- 2026
- Basmat Tech, Riyadh
Results
- Annex A controls in one spine
- 93
- Saudi frameworks cross-walked
- 3
- Fully bilingual
- AR / EN
Problem
ISO 27001 projects are usually run across spreadsheets and Word files, so readiness is hard to measure and the Statement of Applicability drifts away from the risk register.
What I built
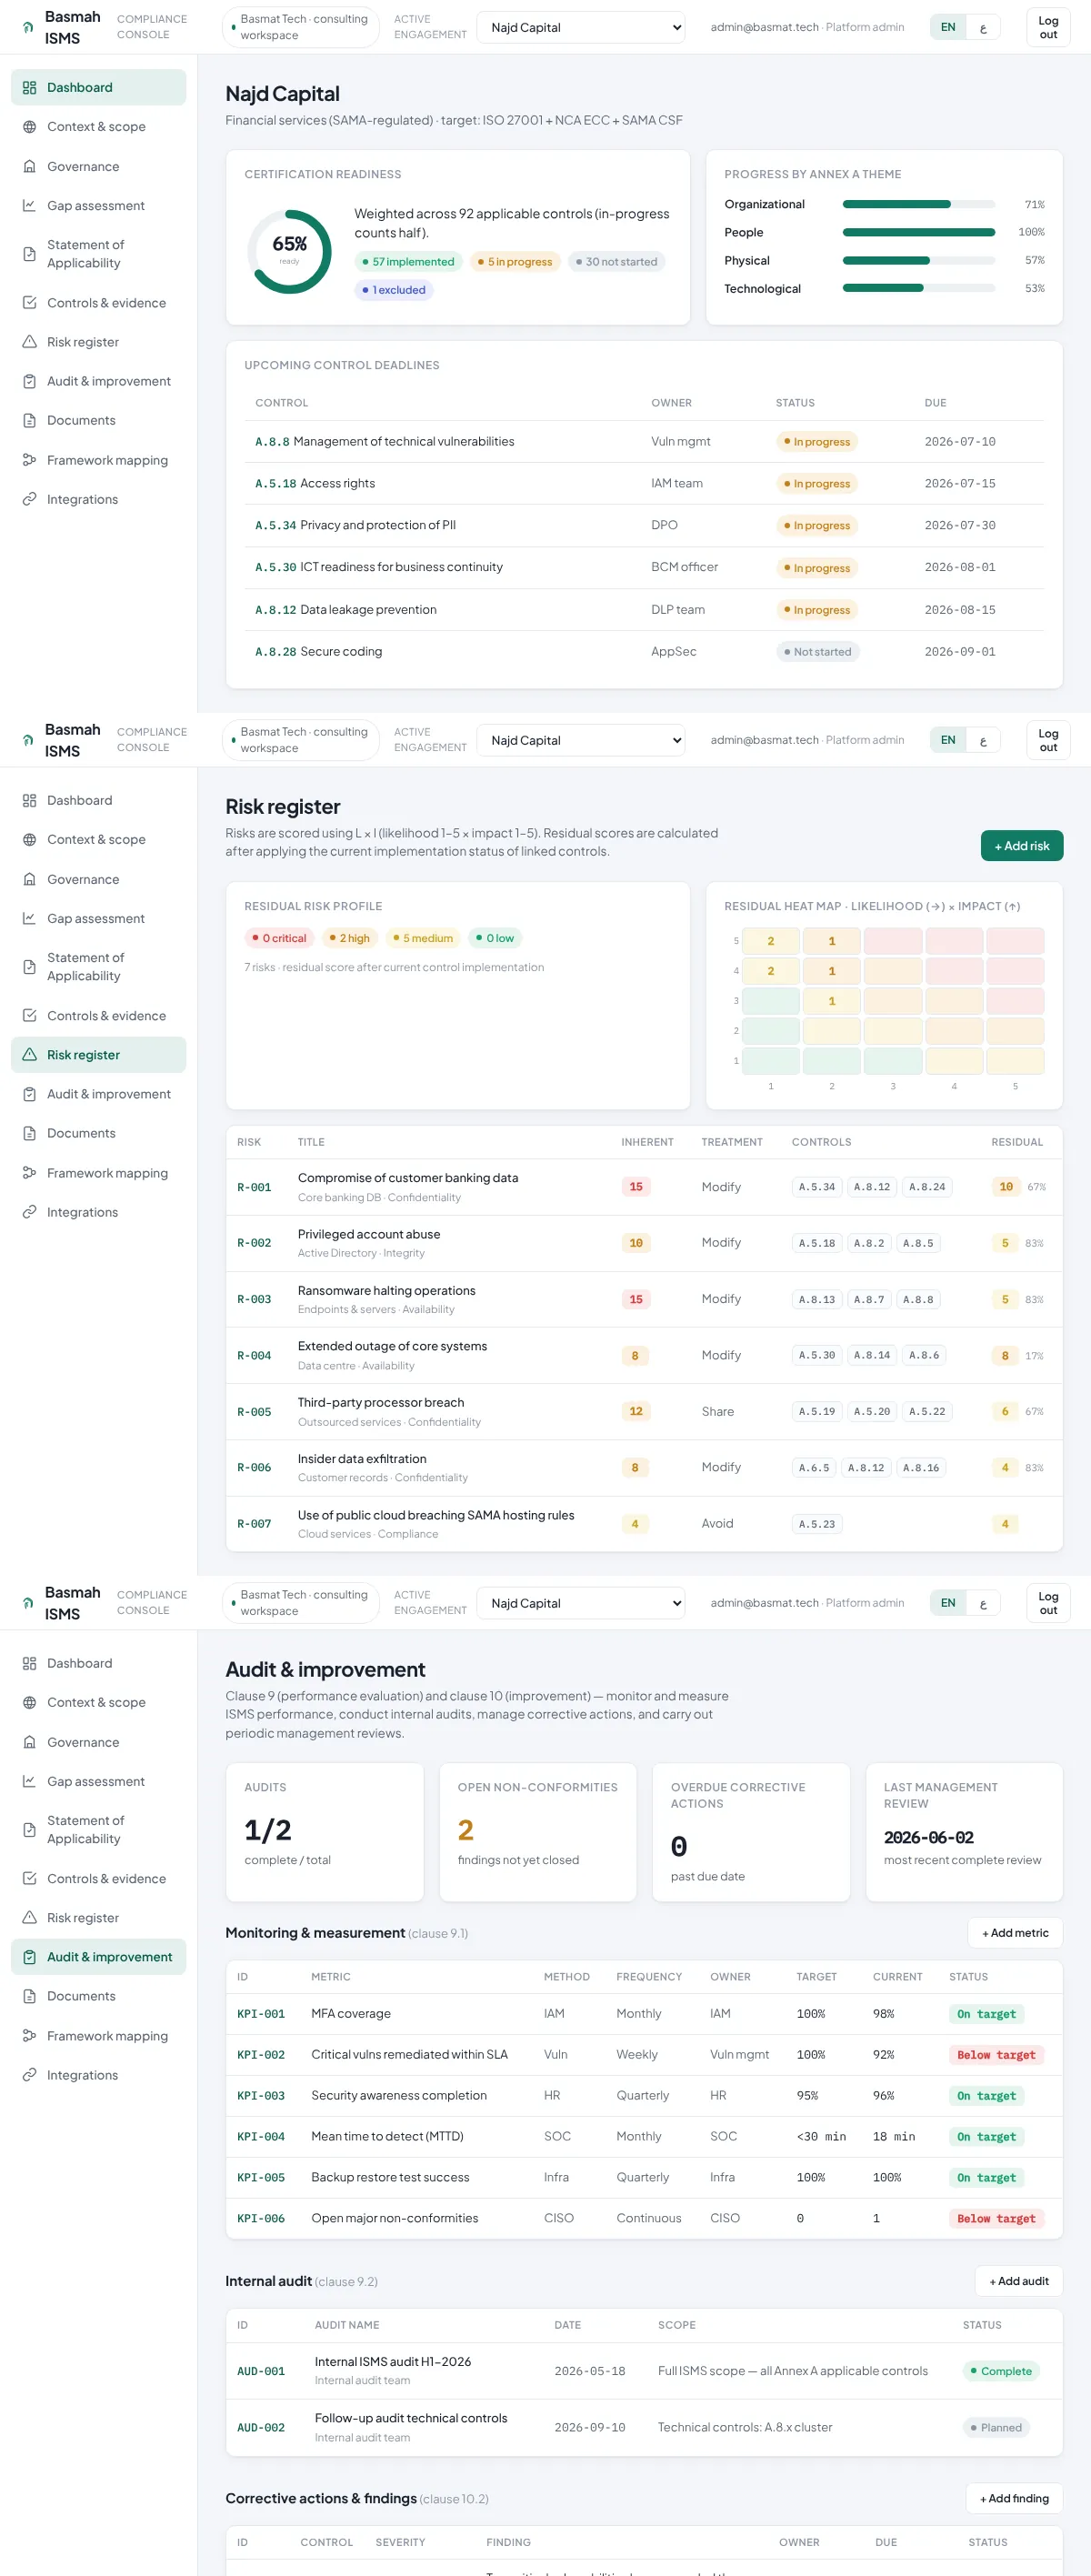
- Built one control spine for all 93 Annex A controls that drives the readiness score, the gap assessment, and the Statement of Applicability.
- Risk register scored by likelihood × impact, with residual risk recalculated from the real implementation status of linked controls and shown on a heat map.
- Cross-walked every ISO control to its NCA ECC, NCA CSCC, and PDPL equivalent for Saudi clients.
- Read-only integrations with Microsoft Entra ID, Intune, Defender, and Azure to collect evidence automatically.
- Firm-level workspaces with roles for platform admins and lead consultants, and signed, httpOnly session cookies.
How it works
- Scope & context
- Gap assessment
- Risk register
- Statement of Applicability
- Audit & certification
Stack
- Next.js
- React
- TypeScript
- Microsoft Graph
Key decisions
The SoA is derived, not typed
Applicability and justification come from the risk register: a control is applicable when a risk treatment needs it, so the SoA can never contradict the risk analysis.
Read-only integrations
Evidence connectors only request read scopes and never write back, which keeps the console safe to connect to a client's production tenant.